






A website can be opened quickly in different countries, protect user accounts and continue to trade on busy clocks. For this, all work is determined from the beginning to where to do. Common content is presented at a close point to the user. Session, balance and payment transactions are walking through the application that confirms authorization and records.
We take the hosting over the way it monitors a request from the browser. First we look at how the content reaches the user, then how the app controls the request. In recent sections there is server access, Fail2Ban and return from backup.
When a user opens the page, open visuals and style files can be presented from the web server. Personal transactions such as session, balance or support request are evaluated in practice, necessary records are taken from the database. Conducting these tasks in the right place reduces doing the same work again for each visit. For example, when a common news visually comes from cache, the user’s private support passes through access control.
Plesk The PHP version and working pools that the app uses over it can be managed. Database connections, file permissions and backups must also be arranged according to the needs of the service. Proper hosting of a store does not only cover the opening of the home page. When the payment notice comes, the order is saved, the execution of delivery to the game server and the user's support the same service parts to reach the record.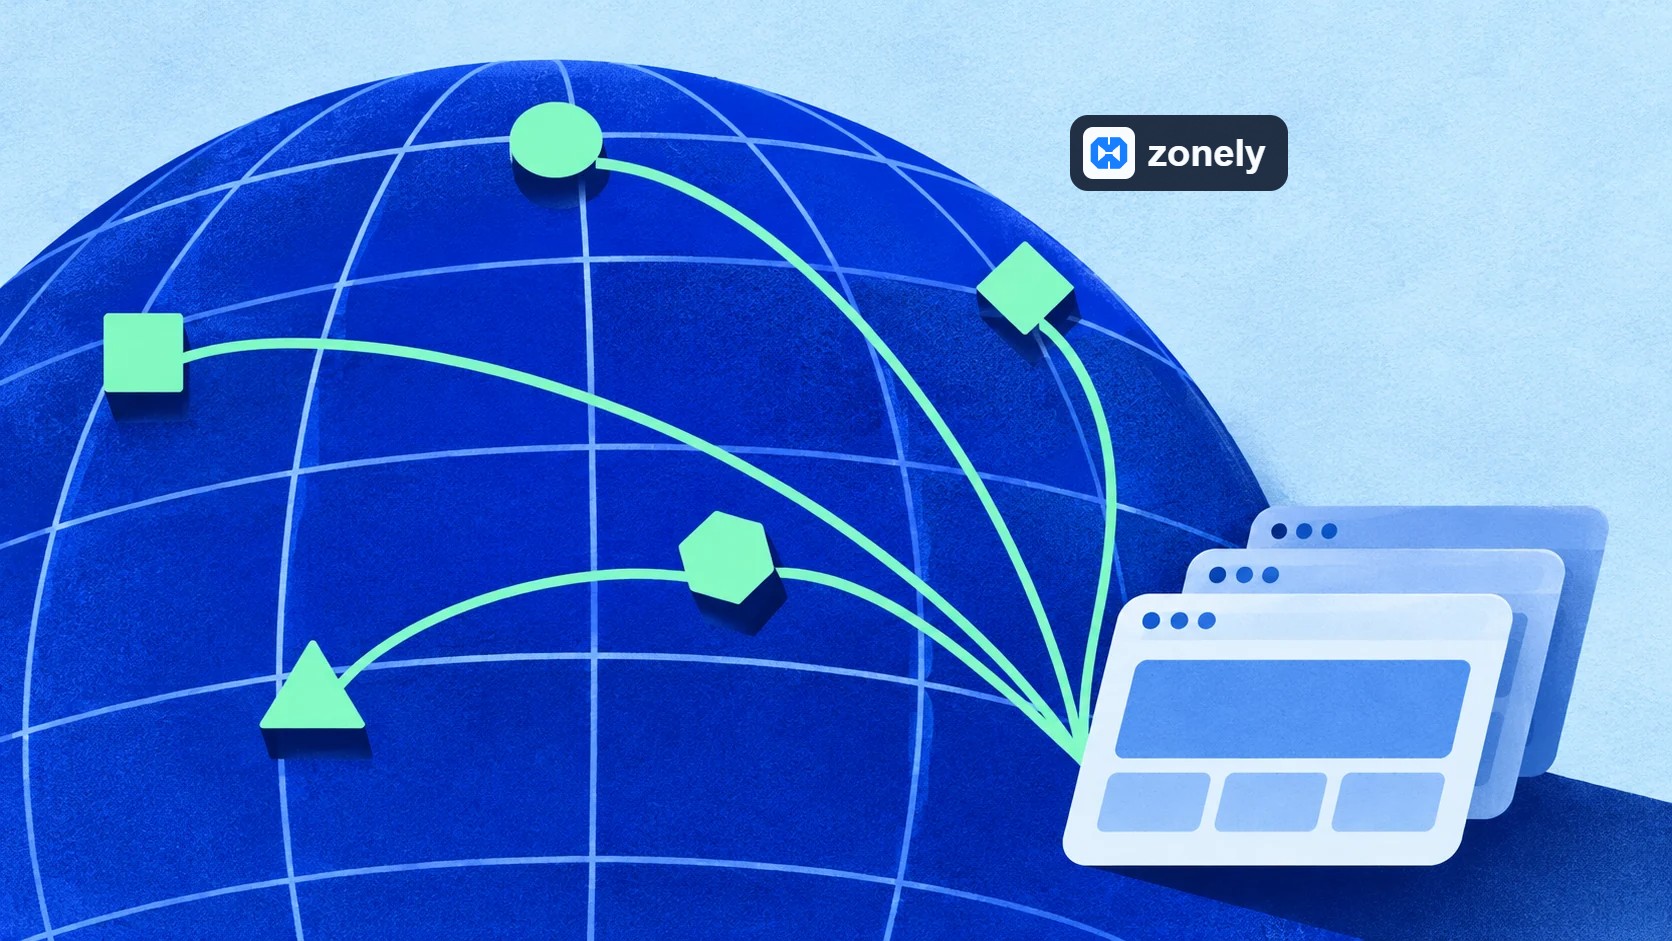 The common content is carried out in the application of session transactions when presented from different regions.
We deliver traffic to users in different countries by meeting the location that is appropriate to be requested. Common content such as logo, style file and open visuals can be presented from a close point to the user. Thus, it does not need to go to the host server for each image. The fast route for the user in one country may not give the same result in another country The first response time should be measured from different regions.
The session panel walks through the authorized application of balance and payment transactions. For example, the same product visual can be presented from cache in multiple countries. If the user is credited, the transaction is processed to the main order record and the new balance is shown only on its own session. With regional traffic distribution, access limits of the user’s private data are maintained together.
For example, when accepting an open search page text, the file upload address is waiting for a specific type of POST request alone. The dies to run script in the search box are checked. In File loading address, methods, body size and number of files are limited. A modeSecurity rule must be tracked on a matching area and selected action daily. Response side If it is supervised, which types of content should also be determined. A bulk print or database error detail that leaks out on the fault screen of the application. The app should keep their error responses simple, write diagnostic details specially.
OWASP Core Rule Set (CRS) converts matches to points on the installations used to rated anomalies. For example, with a suspicious header, the attack die in the body can score together in the same request. The total score is blocked when it reaches the configured threshold. The rule IDs indicate which matches the score. If there is another layer of network in front of the firewall, each case each It is necessary to test the dynamic request in a way that really goes through auditing.
When blocking is activated, the valid transaction should be re-tested to the corrupt request and high traffic scenario. The reason for decision on logs must be seen, password, payment data and connection switches should be masked. The error rate that real users receive between the results to be monitored is the number of blocking and the response time in busy hours. When a rule set stops the attack, the payment will be taken It should also complete the notification, support message and file upload correctly.
Plesk ModSecurity guide · OWASP CRS anomaly rated · OWASP CRS mismatches and rule exceptions
Let’s assume that a Friday evening has hundreds of requests in one minute of an IP. The requests are going to open visuals to everyone, most of them are met from the cache, and if the incorrect number of entries is not increased, users can immediately cool the IP from the game. If the same IP is called password on hundreds of different accounts at short intervals, the speed limit is meaningful for the entry path. First in observation mode, which is in the mode Read the match of requests, then apply verification or blocking for certain time. Get the finish time and withdrawal path of the rule.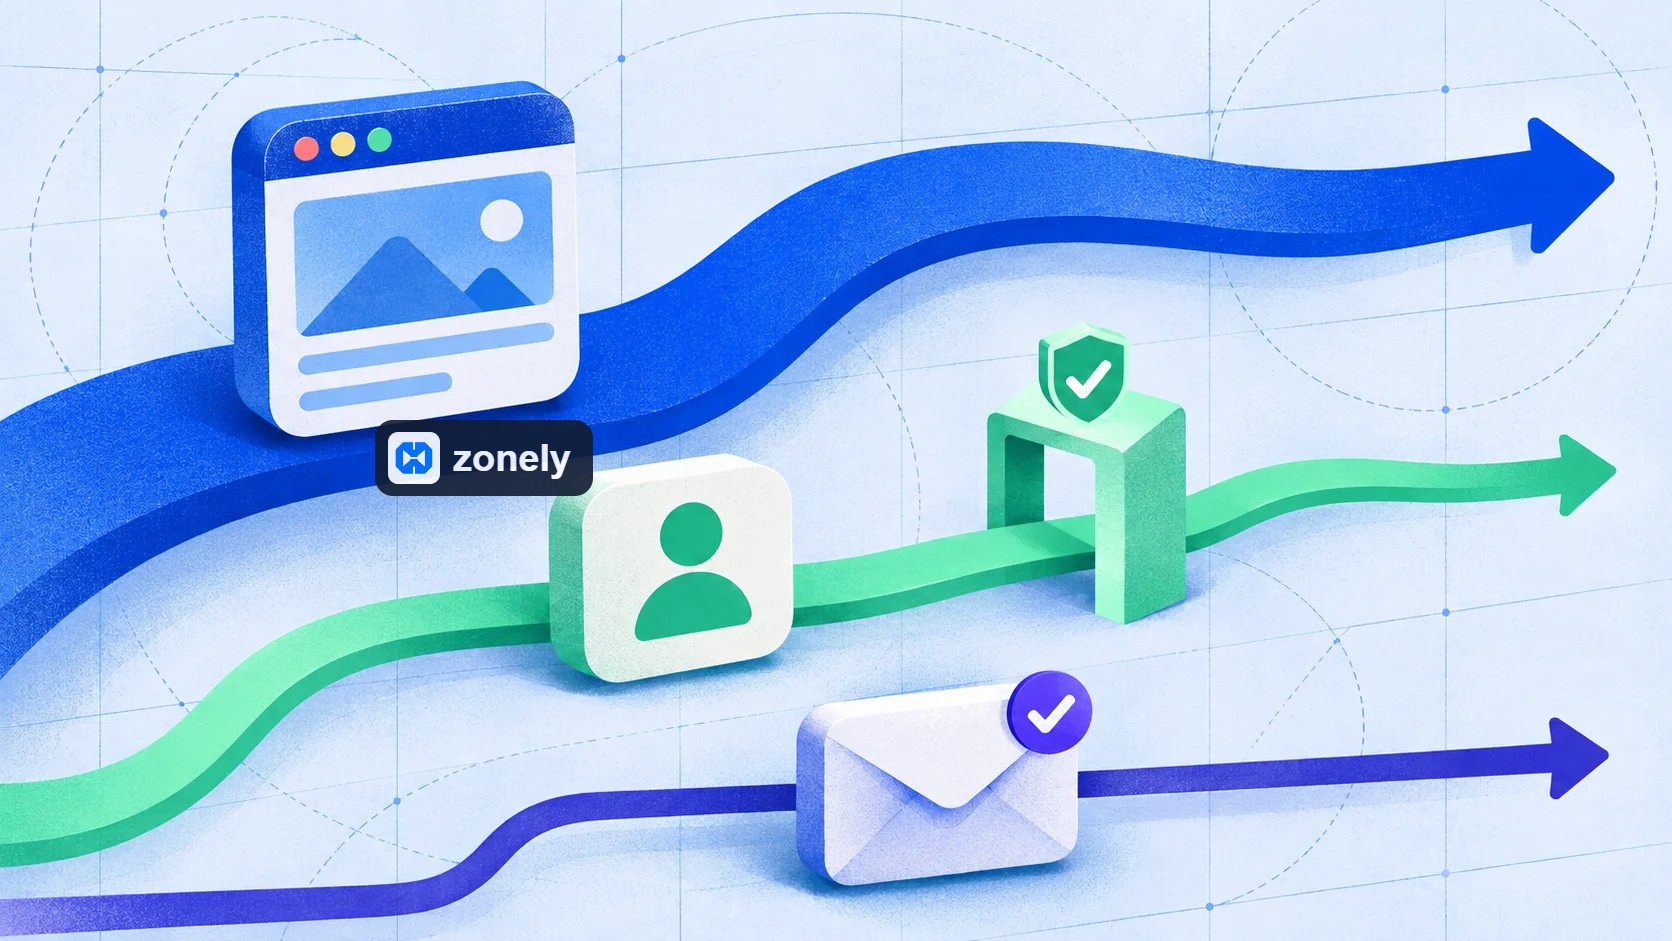 The open page to everyone, the session panel and payment notice pass through different controls.
Safety rules are all flow coverage from the request entrance to the user. The request method accepted by each end point, fields, data types, lengths and body size should be determined. Unforgettable areas should not be processed, invalid requests should be rejected without starting the related process. For repeated trials from the same source, the processing type is appropriate for proper speed limits should be defined.
Checking a POST request is not enough alone. Even if the request comes from an authorized user, another user should change its record. CSRF check should be applied in data exchange transactions with browser session. The incoming values must be linked to query as parameters and coded according to the binding used when written on the page. The permitted rich text The content should be verified with an open label and attribute list. Thus, a value stored in the input does not turn into content running script on another screen that is then displayed.
The purpose of recording the text written by the user is not to delete any special character. In a support message 5 < 10 It should be stored as expression and read on the page. The same value is coded in HTML, while it enters the database query as parameter. JSON response also written with JSON encoder. With a single “clean” function, all these contexts work to solve, both disrupt real messages, leaving some screens.
httpOnly is used in PHP session cookie. When HTTPS is used, Secure is also enabled. The JavaScript in the httpOnly browser limits its cookie directly to read. Secure cookie allows it to be sent via HTTPS. The IP pairing limits the reuse of a captured token from a different address. Cookies settings, MVC output coding and log in on the server so it works together.
Changing the name, content is meaning with blocking controls to run in the area of verification and loading. Not only shorten the name of the file, but a executable content shown as picture does not bring safe. Recoded the verified visual and only offered the expected type is part of the loading line.
The installation component addresses CGI, shell script, JavaScript and PHAR as executable content alongside commentable extensions such as PHP and PHTML. The script protection in the general file processors can handle these types as plain text and add .txt on behalf of the file. The visual upload area rejects the file that does not comply with its permission MIME list. Thus, the overall file will be addressed as a generic file. does not mean that the processors can store a text file, the same file will be considered visually.
The task of the installation area is also important. With the ordinary user visual field, it is not necessary to have the same file policy, which is included in the design presence of the authorized person. In the reviewed protection flow, there are general loading constraints and controls specific design areas. This does not mean that every SVG is accepted; even in the permitted area, the content of the file has audited.
In case of an error during the predisposition production, it is necessary not to open to everyone in part. Save on the temporary space and move the output from the final name. Set the size limit both on the web server and on the PHP side. For example if the application puts 4 MB limit, then the server in front of it accepts much larger bodies, even the file that will be rejected will be rejected, even the bandwidth of the tape and the temporary consumes storage. Give a clear message to the user in the request exceeding the limit which you can try again.
The editable theme and panel files belong to the presentation layer. The template controller can be operated by PHP labels, script commenter headers and directly blocks SQL dies attached into appearance. Even with file name .php, the content is subject to these rules. The template engine compiles the verified template to its own working format. The dynamic data is authorized to the presentation side of the backend the component gives. The raw output directive is restricted, the asset paths are also relative and limited with allowed directories.
A theme may show the title of the support request. The header decides backend to which user will be shown and what records from the database will be withdrawn. If the theme file is directly authorized to read files from the server or open a network connection, then the effect of a design change extends to the data of the store.
The template compiler works for standard values HTML output, codes special characters and nails. For example, the <script> in an input appears as text to the user when written in HTML text field. The raw value of the template is also blocked in source control. In areas where rich HTML needs are clearly used uç backend blocks. If a value is used as URL, The allowed link chart should also be applied to the secure JSON encoding if it is transferred to JavaScript as data.
The work copy scans the content before it is taken into the active template. Shell call, file reading or index listing, access to media variables, cURL and socket operations are examples controlled in this layer. Blocked change will not be written into the enabled template. A valid session opening with SFTP allows file transfer. If the site is activated by that file, the template check decides.
A HTTP client can send request to a address where the server is accessible. The authorization to start a process is commanded to the operating system. These authorities must be limited separately. In addition to code review, process permissions, file access and network output should also be restricted by the task of the plugin.
Management and support screens should show the necessary information for the process as the connection does not work. The open value of the password should not be included in these screens or error responses. With the solving switch, the encrypted registration must be kept separately and limited to the process that creates access to the key. This access separation eliminates the need to see the password on daily support transactions.
Plesk’ built-in input protection limits fail entries from the panel and API. Admin access can also be opened to certain IP addresses or networks. Accounts that don’t need remote connections in the database may be limited to local access. If a separate application server is connected, only access to the relevant database account is given from the source required.
ModSecurity evaluates an HTTP request content. Fail2Ban processes IP level according to the events that are seen on their service logs. Since they can share the same IP multiple people, threshold and obstacle duration should be adjusted according to the service, obstacles must be monitored from daily.
Plesk Fail2Ban and input protection · Manager access limitations · Database access rules
When users say “site frozen” the first distinction is where the response is expected. Open result page for everyone is quick, start from SQL queries that work at the same time comparing the panel of the user who has logged in. If static picture is slower then network, disk or server capacity should also be reviewed. All employees in PHP pool are waiting to respond slowly from an external service, CPU usage is low Even if new requests remain in order. Increasing the number of employees can grow narrowness by sending more simultaneous queries to the database.
For example, you can calculate the outcome table once again and offer a partner for short time instead of recalculation for each user. The corresponding “My account” page and basket are special to the user. After changing the cache rule, open the same address with two different test accounts. If the second user sees his first user’s name, balance or cart, performance is available For example, data has been revealed. Do not complete the test by looking at the opening time of the page.
The last prova is simple: send the wrong type of file, upload a valid small photo and open the result table of a normal user at this time. Then restore the backup to a separate environment. This four process shows that a protection rule does not block and block the user and save what after a real event.
OWASP file upload guide · Cloudflare verification pages
We take the hosting over the way it monitors a request from the browser. First we look at how the content reaches the user, then how the app controls the request. In recent sections there is server access, Fail2Ban and return from backup.
Plesk Starting with the hosting layout
A community site, store and support panel; application files, databases and services running these two. We are hosting in the management of this layout Plesk We use. Connecting the domain name to the site, certification management, web server and operation settings of the application are addressed in the same management layer. The store that user sees is the face that opens out of this scheme.When a user opens the page, open visuals and style files can be presented from the web server. Personal transactions such as session, balance or support request are evaluated in practice, necessary records are taken from the database. Conducting these tasks in the right place reduces doing the same work again for each visit. For example, when a common news visually comes from cache, the user’s private support passes through access control.
Plesk The PHP version and working pools that the app uses over it can be managed. Database connections, file permissions and backups must also be arranged according to the needs of the service. Proper hosting of a store does not only cover the opening of the home page. When the payment notice comes, the order is saved, the execution of delivery to the game server and the user's support the same service parts to reach the record.
How quickly does your website open in different countries?
The common content is carried out in the application of session transactions when presented from different regions.We deliver traffic to users in different countries by meeting the location that is appropriate to be requested. Common content such as logo, style file and open visuals can be presented from a close point to the user. Thus, it does not need to go to the host server for each image. The fast route for the user in one country may not give the same result in another country The first response time should be measured from different regions.
The session panel walks through the authorized application of balance and payment transactions. For example, the same product visual can be presented from cache in multiple countries. If the user is credited, the transaction is processed to the main order record and the new balance is shown only on its own session. With regional traffic distribution, access limits of the user’s private data are maintained together.
Web requests reach server
How to read ModSecurity rule?
PleskModSecurity, used for web application firewall in , controls HTTP requests with structured rules. The set of rules describe which process will look at what area, what matches and matches. A rule can only examine the way and method of request. Another rules may be divided into form areas, separated JSON values or structure of installation The request headers are read at the early stage; the body control is done after the content is separated. It is necessary to verify that the appropriate separationr works for a endpoint using JSON or file upload.For example, when accepting an open search page text, the file upload address is waiting for a specific type of POST request alone. The dies to run script in the search box are checked. In File loading address, methods, body size and number of files are limited. A modeSecurity rule must be tracked on a matching area and selected action daily. Response side If it is supervised, which types of content should also be determined. A bulk print or database error detail that leaks out on the fault screen of the application. The app should keep their error responses simple, write diagnostic details specially.
| Rule family | Denetated sample | Complete control in the application |
|---|---|---|
| Add-on and XSS | Betic labels, event attributes and executable connection schemes | With HTML text, attribute or URL context. Limit rich text with permitted items. |
| SQL injection | syntax to change the structure of form value query | Use parameter query. Select options from fixed list, which determines the query structure like ranking column. |
| Road migration and file access | Requests trying to go out of the application directory or achieve special configuration | Install the file path from user input. Verify registration ID and open the file from the allowed store. |
| Command injection | Special separators and unexpected scripts for system commands | Combine user data to shell command. Validate processing and parameters separately. |
| Shape and size | Broken form or JSON, unexpected method and excessive large body | Stop the operation in discrete error. Identify type, fields and size accepted by each end point. |
Evaluate the request in context instead of blocking by single word
In a support message, the word “script” or “select” is usual. For example, a user can send technical error text. The audit should look at what field and in which structure of the word. With script tag from a plain text field, the code sample shown as text in a support message does not give the same result. How to solve coded inputs It is also important. With the firewall, the application may come to a different understanding in the app worth passing through the audit if there are different comments from each other.OWASP Core Rule Set (CRS) converts matches to points on the installations used to rated anomalies. For example, with a suspicious header, the attack die in the body can score together in the same request. The total score is blocked when it reaches the configured threshold. The rule IDs indicate which matches the score. If there is another layer of network in front of the firewall, each case each It is necessary to test the dynamic request in a way that really goes through auditing.
What rule changes if a valid request is blocked?
The new rules should first be tested with real workflows in detection mode or in a test environment. The product saves, support message, visual upload and signed payment notice are individually tried. If a form is accidentally blocked, the request is found on the road and the rule ID. For example, if an authorized design editor is really HTML expected in the only field of the single area, there is no exception alone it is defined for the road, field and relevant rule. In such an exception, the application must undergo its own authorization and content control.When blocking is activated, the valid transaction should be re-tested to the corrupt request and high traffic scenario. The reason for decision on logs must be seen, password, payment data and connection switches should be masked. The error rate that real users receive between the results to be monitored is the number of blocking and the response time in busy hours. When a rule set stops the attack, the payment will be taken It should also complete the notification, support message and file upload correctly.
Plesk ModSecurity guide · OWASP CRS anomaly rated · OWASP CRS mismatches and rule exceptions
Put the managed verification right place
WAF evaluates the known attack patterns with the way, body and other signals that they want. There must be a well-defined rule set, which includes time limit for suspicious browser traffic, Managed Challenge and blocking steps when necessary. It may also belong to dozens of users on the same IP school network. First refer to the road, time interval and unsuccessful trading rate. Game If you put browser verification on the delivery address or payment notice of the plugin, it can not respond to automation. Use the signature, time stamp and processing special speed limit on these ends.Let’s assume that a Friday evening has hundreds of requests in one minute of an IP. The requests are going to open visuals to everyone, most of them are met from the cache, and if the incorrect number of entries is not increased, users can immediately cool the IP from the game. If the same IP is called password on hundreds of different accounts at short intervals, the speed limit is meaningful for the entry path. First in observation mode, which is in the mode Read the match of requests, then apply verification or blocking for certain time. Get the finish time and withdrawal path of the rule.
Request, session and authorization control in the application
The form from the user’s browser is met at the entrance of a gaming plugin and a file upload. In the central controller, the request passes through control layers before starting the corresponding process. The first layer limits the request until the same source will be busy in short time. Separate limits for data-changing requests with general traffic Applicable. When the limit is filled, it will be stopped with a response that informs the request to wait. Thus, it does not have to share the same budget in continuous support request with an ordinary page view.
The open page to everyone, the session panel and payment notice pass through different controls.Rule set to reflect the POST entries and data into the page
The central controller scans the form areas including nested arrays. Deleting the body in the corresponding JSON ends, deleting values. Normalization before the scan ensures that the same input coded in different formats is evaluated with the same rules. Body and area length limits are also controlled. Speed limit determines how often a source can be requested. Content inspection If you look at the data in one request.| Sample seen in the post input | Aim of audit |
|---|---|
| Betic or iframe tag, HTML event attribute, javascript: link | Then prevent code execution in the browser of the input reflected on a page. |
| PHP opening tag, shell exec call or shell command substitution | Blocking content into the text field for code or script execution on the server. |
| A flow wrapper such as attempt to exit the top array or php:// | Cut the input that works to go out of the expected file path or open an alternative flow. |
| UNION structure SELECT, SQL call producing delay or write mold to file | mark the input aimed at changing the outcome of the vine, working time or effect. |
Checking a POST request is not enough alone. Even if the request comes from an authorized user, another user should change its record. CSRF check should be applied in data exchange transactions with browser session. The incoming values must be linked to query as parameters and coded according to the binding used when written on the page. The permitted rich text The content should be verified with an open label and attribute list. Thus, a value stored in the input does not turn into content running script on another screen that is then displayed.
| Home | The rules to be defined | Expected behavior |
|---|---|---|
| Request input | Method, size, space and type limits | Non-valid request is rejected before the process. |
| Transaction authority | Log in, registration and CSRF control if required | The user is only authorized to register. |
| Database | Parameter query and minimum required access | The user input cannot change the structure of query. |
| Output | Linking appropriate coding and rich text | The content does not work unwanted code while being shown. |
| Intense traffic | End point-based speed limit, verification and periodic blocking | The suspicious use is limited, the normal way of operation is maintained. |
We do not determine the safety limit in the form boxes
A moderator adds screenshot to 471. If the server looks like a solo session, the user can add files to another user's request by making 471 in the request. Even if the file is an impeccable PNG here. Verify that the person who log in first is entitled to access that request, then the addition authority. Finally, the file itself of the file itself is unauthorised. Review. Identity, transaction permission and file type are three separate controls.The purpose of recording the text written by the user is not to delete any special character. In a support message 5 < 10 It should be stored as expression and read on the page. The same value is coded in HTML, while it enters the database query as parameter. JSON response also written with JSON encoder. With a single “clean” function, all these contexts work to solve, both disrupt real messages, leaving some screens.
What happens if the session cookie is used from another IP?
When the web account is verified, the server log token controls the IP address recorded in the login and the last validity time. If someone copys the token and sends it from a different IP, the session will not match the registration and the request is not authorized by that account. The same rule may require re-enter if the user changes IP from mobile data to Wi-Fi.httpOnly is used in PHP session cookie. When HTTPS is used, Secure is also enabled. The JavaScript in the httpOnly browser limits its cookie directly to read. Secure cookie allows it to be sent via HTTPS. The IP pairing limits the reuse of a captured token from a different address. Cookies settings, MVC output coding and log in on the server so it works together.
File upload and secure storage
How do you understand that a picture is really picture?
The MIME header sent by the browser can be changed. Put the size limit on the installation line, check the allowed extension, type from the file content and open the visual with a picture library. Limit the number of pixels. When a small compressed file is opened, it can consume too much memory. Recode the uploaded image and store the server produced by the name. Loading In the directory, PHP should not be operated, there must be a control of ownership in downloading special files.File name generated by double extension and system
Name of a file image.php.png It can be. Finally, the PNG write cannot prove that the data inside is picture. It is important so that the file type and visual structure are corrected during installation. If a real PNG pass the verification, the identification of the system is used instead of the original file name in supported visual recording streams. For example, stored file 8d7c42f1.png is called a single visual extension in the format. The parts that the user add to the file name does not determine the name of the file on the server.Changing the name, content is meaning with blocking controls to run in the area of verification and loading. Not only shorten the name of the file, but a executable content shown as picture does not bring safe. Recoded the verified visual and only offered the expected type is part of the loading line.
The installation component addresses CGI, shell script, JavaScript and PHAR as executable content alongside commentable extensions such as PHP and PHTML. The script protection in the general file processors can handle these types as plain text and add .txt on behalf of the file. The visual upload area rejects the file that does not comply with its permission MIME list. Thus, the overall file will be addressed as a generic file. does not mean that the processors can store a text file, the same file will be considered visually.
How to deal with scripts stored in SVG?
SVG describes the drawing with a text-based structure. It can be added to a scriptural, incident triggering attribute or dangerous connection into the structure. The file may carry content that will change page behavior within appearing like a small logo on the screen. Therefore, the system also examines the contents of SVG. The script labels, event processors, dangerous link schemes and embedded active ingredients are controlled examples. Non-convenient installation is blocked without being processed.The task of the installation area is also important. With the ordinary user visual field, it is not necessary to have the same file policy, which is included in the design presence of the authorized person. In the reviewed protection flow, there are general loading constraints and controls specific design areas. This does not mean that every SVG is accepted; even in the permitted area, the content of the file has audited.
Who can access the file when installation is completed?
It can be open to the public for everyone, if the screenshot requesting support may contain the user's email address. Both of them should not be the same as the rules of storage and offering even if there are images. Keep the support attachment outside the web root, check that the user still has access to the corresponding demand in the request of downloading. A difficult file name to guess is one-stop access control Do not use it. You can present the public as a recoded, non-operable visual.In case of an error during the predisposition production, it is necessary not to open to everyone in part. Save on the temporary space and move the output from the final name. Set the size limit both on the web server and on the PHP side. For example if the application puts 4 MB limit, then the server in front of it accepts much larger bodies, even the file that will be rejected will be rejected, even the bandwidth of the tape and the temporary consumes storage. Give a clear message to the user in the request exceeding the limit which you can try again.
MVC templates and SFTP changes
How to split template and application code with MVC?
We use MVC in our templates. When a store page is opened, the controller will meet the request and determine which records can be accessed. The data layer brings products and prices. The appearance produces the page with product name, price and stock information given to it. Thanks to this distinction, the payment flow or database to change the product card or list layout of a theme No need to change the query.The editable theme and panel files belong to the presentation layer. The template controller can be operated by PHP labels, script commenter headers and directly blocks SQL dies attached into appearance. Even with file name .php, the content is subject to these rules. The template engine compiles the verified template to its own working format. The dynamic data is authorized to the presentation side of the backend the component gives. The raw output directive is restricted, the asset paths are also relative and limited with allowed directories.
A theme may show the title of the support request. The header decides backend to which user will be shown and what records from the database will be withdrawn. If the theme file is directly authorized to read files from the server or open a network connection, then the effect of a design change extends to the data of the store.
What does MVC do when user input is reflected on the page?
The value a user writes to the search box can see again on the result page. There is a risk of XSS that burns if it is shown in the same response. A support message is recorded, and then when it is shown on another screen, the XSS risk is born. In both cases, how the browser will comment the data, determines the appearance of MVC where the output is generated.The template compiler works for standard values HTML output, codes special characters and nails. For example, the <script> in an input appears as text to the user when written in HTML text field. The raw value of the template is also blocked in source control. In areas where rich HTML needs are clearly used uç backend blocks. If a value is used as URL, The allowed link chart should also be applied to the secure JSON encoding if it is transferred to JavaScript as data.
How to activate the template organized with SFTP?
In SFTP sync, the file first comes to a separate work copy for the theme. The sync layer controls that the file belongs to the corresponding theme and is located on an editable pathway. Road resolution prevents directories transitions out of the working area and the target remaining links outside. A new record made in the panel of an old SFTP copy does not crush the file update is also compared.The work copy scans the content before it is taken into the active template. Shell call, file reading or index listing, access to media variables, cURL and socket operations are examples controlled in this layer. Blocked change will not be written into the enabled template. A valid session opening with SFTP allows file transfer. If the site is activated by that file, the template check decides.
What work authorizations should be given to a plugin?
The task that a plugin working on the server side is limited. If a add-on formats the product list, there is no need to change or link out file permissions. Different ways reaching the same authority should be discussed together while the restrictions are determined.| Authorization area | Methods of use to be reviewed |
|---|---|
| Command execution | Direct shell call, command substitution or separate operation system process start. |
| Code execution | Generate code from text, upload code from file, indirect or dynamic call. |
| Network access | read data via HTTP request, direct socket, file transfer client or network with cURL. |
| File system | File reading and writing, index listing, link creation or change permission. |
| Application environment | Reading environment variables, changing operating settings or access common application status. |
Server access and connection information
Where to use Database password?
The app needs a valid password to connect to the database. In the connection flow we review, the password is stored in the server encrypted and resolved by the application process that connects the link. Thus, seeing a configuration record cannot be read the database password alone.Management and support screens should show the necessary information for the process as the connection does not work. The open value of the password should not be included in these screens or error responses. With the solving switch, the encrypted registration must be kept separately and limited to the process that creates access to the key. This access separation eliminates the need to see the password on daily support transactions.
PleskFail2Ban and access protections in
On Linux PleskFail2Ban, which can be activated in monitors the logs of selected services. The rule defined for each service determines what records will count, how many trials will fill the threshold within which time and how long it is blocked. For example if there are failed entries from the same IP to the SSH, the corresponding rule may temporarily cut the access of the IP on the firewall. Plesk services such as panel, SSH and mail can be viewed with different logs and rules.Plesk’ built-in input protection limits fail entries from the panel and API. Admin access can also be opened to certain IP addresses or networks. Accounts that don’t need remote connections in the database may be limited to local access. If a separate application server is connected, only access to the relevant database account is given from the source required.
ModSecurity evaluates an HTTP request content. Fail2Ban processes IP level according to the events that are seen on their service logs. Since they can share the same IP multiple people, threshold and obstacle duration should be adjusted according to the service, obstacles must be monitored from daily.
Plesk Fail2Ban and input protection · Manager access limitations · Database access rules
Density, backup and return
Plesk, Docker and really quick-opened page
Plesk Separate PHP-FPM pools and memory limits for sites over the site can be managed. In a installation used in Docker, processor and memory limits, read-only application files and separate service IDs limit the effect of a work. The speed of the main page determines concrete works: visual dimensions, database queries and process from waiting for the first response. Get caching of the general pages, Keep the user’s private panel outside the common cache. Monitor the most slow-percent five responses and PHP requests waiting on the tail.What to measure before opening a container?
ZonelyOur goal is to complete every request using as little resources as possible. We monitor the CPU time, RAM usage, disk and network access and data written in the swap field. It relieves processor and discs that do not run the same query anywhere unnecessary. Keeping the cache limited balances RAM consumption. To complete a request with less memory, we are constantly looking for the swap area can extend the response. It shows the response time and error rate in intensity along with resource consumption that a change does not work.When users say “site frozen” the first distinction is where the response is expected. Open result page for everyone is quick, start from SQL queries that work at the same time comparing the panel of the user who has logged in. If static picture is slower then network, disk or server capacity should also be reviewed. All employees in PHP pool are waiting to respond slowly from an external service, CPU usage is low Even if new requests remain in order. Increasing the number of employees can grow narrowness by sending more simultaneous queries to the database.
For example, you can calculate the outcome table once again and offer a partner for short time instead of recalculation for each user. The corresponding “My account” page and basket are special to the user. After changing the cache rule, open the same address with two different test accounts. If the second user sees his first user’s name, balance or cart, performance is available For example, data has been revealed. Do not complete the test by looking at the opening time of the page.
What time will the store remain when it comes back to backup?
Think you lost payments from morning 03.00 or lunch. The provider has received the money and several prizes to the game can be delivered. Some rewards that run immediately on the old database may distribute second time. Open the restored store in isolated environment before. Compare the subsequent payment and delivery IDs of the backup, then set missing orders, then select queue restart. The recovery prova for a community site is more valuable than the control of "backed" alone.The last prova is simple: send the wrong type of file, upload a valid small photo and open the result table of a normal user at this time. Then restore the backup to a separate environment. This four process shows that a protection rule does not block and block the user and save what after a real event.
OWASP file upload guide · Cloudflare verification pages




“I give it 10 out of 10. Even other software doesn’t offer this many features.”